Lesson Overview
This video, presented by Rainié Papadopoulos, explains how to raise a defendable nonconformity in compliance with ISO 13485.
Objective & Standards Referenced
- The goal is to raise clear, easily understood, and defendable nonconformities.
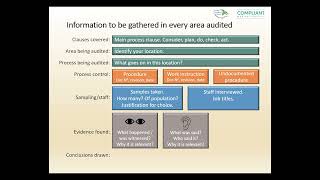
- Audit results must include identification of relevant processes and conclusions.
- Key Standards:
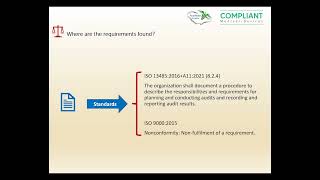
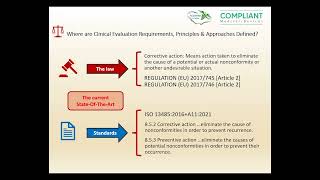
- ISO 13485 – Defines internal audit requirements.
- ISO 9000 – Provides the definition of a nonconformity.
The Three-Step Approach to Raising a Nonconformity
- Step 1: Describe the Context & Magnitude
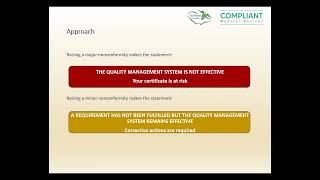
- Clearly explain what the nonconformity is and how serious the breach is.
- Step 2: Identify the Breached Clause
- Provide the numerical reference and exact wording from the standard.
- Example: A purchasing procedure is generally acceptable but does not consider supplier risk in relation to the medical device.
- Step 3: Document Objective Evidence
- Ensure the finding is backed by clear, objective evidence.
- Example: Supplier selection follows stringent criteria, but there is no documented evidence that device risk was considered.
Final Takeaways
- A well-documented nonconformity should be objective, clear, and concise.
- It should remove subjectivity from the audit process.
- It helps the person responsible for addressing the issue by providing actionable information.